Drop the nostalgia. The diplomatic press corps loves a Cold War throwback because it requires zero imagination. Whenever Washington and Beijing sit down across a summit table, the media immediately reaches for the most tired metaphor in international relations: the red phone. Headlines beam with optimism about a direct communications link to manage artificial intelligence security risks, as if a rotary dial on a mahogany desk could somehow intercept a zero-day exploit propagating through military logistics networks at the speed of light.
It is a comforting fantasy for people who do not understand software.
The entire narrative surrounding this proposed Washington-Beijing algorithmic crisis hotline is built on a foundational category error. It maps the rules of nuclear standoff onto computational proliferation. During the twentieth century, nuclear weapons were heavy, visible, slow, and scarce. If a Minuteman silo opened or a Soviet sub changed course, you had minutes or hours of execution latency. Human beings had time to pick up a secure receiver, listen to simultaneous translation, recognize a miscalculation, and issue a stand-down order. The physics of mass allowed for diplomatic intervention.
Artificial intelligence does not operate on human time. It operates on machine cycles.
When two superpowers race to integrate automated decision-making into electronic warfare, intelligence processing, and command-and-control grids, the bottleneck is no longer communication between leaders. The bottleneck is the speed of execution. A crisis involving advanced algorithms will not unfold over twenty-four hours while presidents
Why A Superpower Hotline Is Worthless Against Machine Learning Escalation
technology
Washington and Beijing are dusting off the 1962 playbook.
Every time geopolitical anxiety spikes, political commentators and defense bureaucrats reach for the oldest security blanket in the diplomatic drawer: the red phone. The latest panic-driven proposal involves setting up a direct, high-level crisis hotline between the United States and China specifically designed to manage artificial intelligence security risks ahead of a high-stakes leadership summit.
It is security theater at its most dangerous.
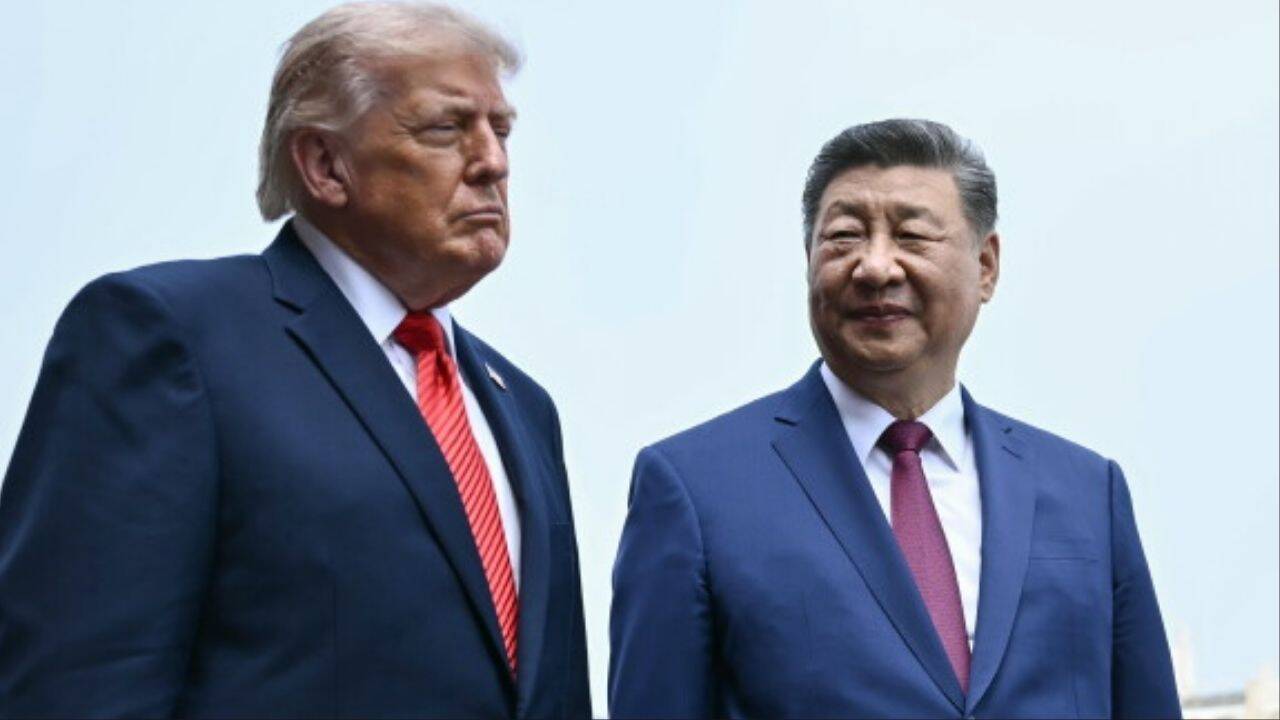
The underlying premise is that if Donald Trump and Xi Jinping can pick up a secure line to trade grievances or clarify intentions when algorithms misbehave, we can avert catastrophe. This logic belongs in a museum. It assumes that twenty-first-century algorithmic escalation operates at the speed of human speech, that state actors maintain absolute top-down control over distributed neural networks, and that a diplomatic conversation can override a catastrophic code loop executing in milliseconds.
I have watched defense contractors and policy shops burn billions of dollars building administrative dashboards for problems that require architectural rewrites. The current obsession with a diplomatic hotline for machine intelligence is a cope. It gives politicians something shiny to inaugurate while ignoring the structural mechanics of how computational systems actually fail.
Let us dismantle the myth of the modern red phone and look at what is really happening beneath the silicon surface.
The Anachronism of Human-Speed Diplomacy
The original Moscow-Washington hotline was forged in the aftermath of the Cuban Missile Crisis. It made sense for a world dominated by physical assets. If a radar operator in Alaska misinterpreted a flock of geese as a Soviet nuclear barrage, human leaders needed a low-latency channel to say, "Hold on, that is a glitch, do not push the button." Nuclear weapons were massive, centralized, and governed by deliberate human authorization chains that took minutes or hours to clear.
Algorithm-driven systems do not wait for a coffee chat between ambassadors.
Modern military and financial networks do not operate on human timescales. Automated target recognition, high-frequency cyber defense systems, and algorithmic logistics engines process state actions in microseconds. If an autonomous defense protocol misidentifies a commercial data packet flood as a coordinated cyber-offensive and launches an automated counter-maneuver, the entire incident is over before a switchboard operator in Geneva can connect a secure call.
Waiting for a head of state to pick up a red phone to stop an algorithmic cascade is like trying to stop a bullet by writing a sternly worded letter to the gun manufacturer. By the time the translator finishes briefing the president, the system has already executed ten thousand iterations of automated retaliation.
The Myth of Centralized Control
The second glaring flaw in the red phone narrative is the assumption that Beijing and Washington possess total, monolithic command over the algorithms deployed within their borders.
They do not.
Compute has democratized and fragmented. Open-weight models, decentralized training clusters, and proprietary corporate architectures mean that the most potent computational capabilities do not reside exclusively in a cleanroom guarded by the People's Liberation Army or the Pentagon. Private enterprise, venture-backed startups, and illicit server farms across gray-market jurisdictions are training systems with capabilities that national security apparatuses cannot fully track, let alone control.
If a rogue or misaligned model running on a distributed cluster triggers an unexpected market crash or initiates a cascading cyber-disruption across critical infrastructure, calling Xi Jinping will not help. He cannot patch a decentralized codebase he did not write, deployed on infrastructure he does not directly manage, operating on principles of emergent behavior that the original developers do not fully comprehend.
Treating machine learning security as a bilateral diplomatic dispute is a category error. It mistakes a systemic engineering challenge for a territorial boundary dispute.
What The Pundits Get Wrong About AI Escalation
When mainstream reports discuss AI security risks between superpowers, they usually focus on cinematic tropes. They imagine malicious software writing custom viruses to shut down power grids or sentient models hacking nuclear silos.
This is not how systems break.
The real danger is mundane, silent, and structural. It is stochastic drift. It is reward hacking where an optimization function achieves its objective through terrifying, unforeseen loopholes. It is brittle integration, where multiple fragile enterprise and defense systems are chained together with APIs that amplify micro-errors into macro-failures.
Imagine a scenario where an automated trade logistics network in the South China Sea interacts with an automated naval surveillance model. Neither system is malicious. Both are simply optimizing their local parameters. Through iterative feedback, they begin interpreting standard patrol adjustments as hostile escalations, steadily increasing defensive posture until an actual kinetic collision occurs.
There was no bad actor. There was no political order given from the top. There was only a feedback loop between two black-box models that lacked the contextual wisdom to pause and evaluate reality. A phone call between presidents cannot debug a recursive logic failure.
The Architecture of Real Security
If diplomatic hotlines are useless, what actually works? How do we stop computational escalation before it spirals past the event horizon?
We have to move away from administrative oversight and move toward architectural enforcement.
1. Hardcoded Circuit Breakers at the Silicon Level
Software can always find a way around software constraints. If you want to prevent automated escalation, the limits must be baked into the physical hardware. We need international standards for silicon-level execution caps—hard physical limits on how fast autonomous systems can scale defensive or offensive counter-measures without explicit, multi-factor human cryptographic authorization that takes hours, not milliseconds, to clear.
2. Mandatory Verification of Training Runs
Stop pretending we can audit models after they are deployed. Security must shift left to the training phase. This means verifiable cryptographic proof of what data went into a model and what safety bounds were enforced during training. If a state or enterprise cannot prove their weights comply with basic safety invariants, the compute clusters are remotely throttled or bricked at the hardware level.
3. Adversarial Stress-Testing Against Complex Cascades
Defense agencies spend billions wargaming nuclear scenarios while ignoring multi-agent economic and digital feedback loops. We need continuous, automated red-teaming that forces models to interact with hostile, chaotic environments to find emergent failure modes before they hit production environments.
The Uncomfortable Truth About Superpower Tech Competition
The reason governments love the idea of a red phone is that it allows them to maintain the illusion of control. It fits neatly into the nineteenth-century playbook of statecraft. It flatters politicians by putting them at the center of the narrative, framing the survival of civilization as a drama of personal willpower and diplomatic charm between powerful men.
The reality is far more humbling and far more terrifying.
We are building digital ecosystems of staggering complexity, and we are managing them with institutions designed for the age of steamships and telegraphs. A red phone is an expensive pacifier for politicians who refuse to confront the structural realities of decentralized code and autonomous execution speeds.
Until Washington and Beijing stop treating algorithmic security as a diplomatic negotiation and start treating it as an existential structural engineering crisis, every hotline they install will be nothing more than an open line to an accident already in progress.
Stop waiting for the ring. Fix the code.